The 90s problem: web application explosion
Back in the 90s, as the web was taking off, a new category of enterprise security products emerged: web access management. It became essential for governing the multitude of web applications corporations were rushing to deploy and secure.
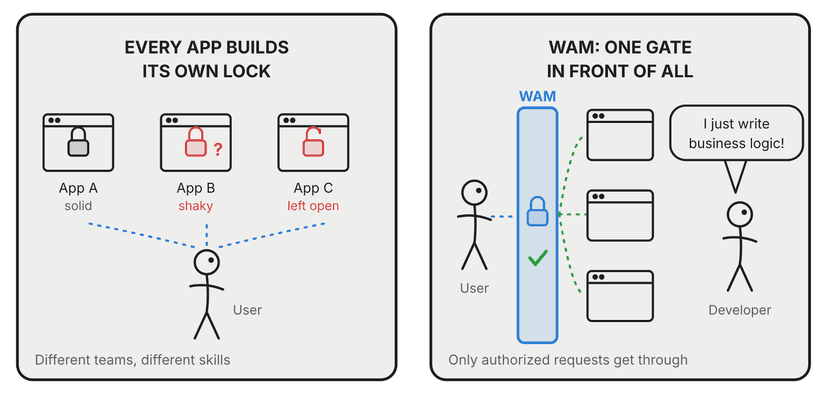
But why was it needed at all? Commercial off-the-shelf (COTS) applications already shipped with their own authentication provisions. Teams building custom applications could write their own authentication and authorization functions into the application. On paper, every application could secure itself.
In practice, though, properly securing an application is extremely tricky. Other than keeping up with the ever-changing security landscape that requires constant attention, different teams bring very different levels of security skill. Some get it right; many get it wrong. Security integration is hard.
What Web Access Management changed
Web access management moved the burden of individually securing each application to an access management tier governed by central policy. Security moving out of the application did not mean not using secure practices to code an application but rather it let developers focus on their applications core business logic and delegated the complex function of properly securing their application to solutions that specialized in securing applications.
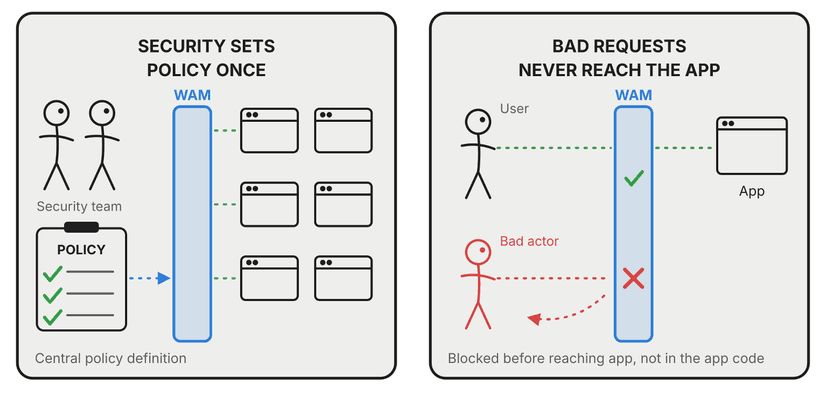
The contract was simple. If a request reached an application, it had already passed through the security layer. Only traffic that cleared authentication and authorization ever got to the app and the app could consume the authorization hints to expose data and views. Security became a property of the infrastructure, not a feature every team had to rebuild.
Web access management was a major win for enterprises trying to secure a growing sea of applications, and it paid off twice:
For developers: relief from the heavy lifting of designing authentication and authorization in every app
For corporate IT security: one place to define policy that was enforceable and auditable so that application could be secured and governed centrally.
The approach became standard. Few Fortune 100 organizations ran without an access management solution. Mention SiteMinder to an enterprise security team and they will recall protecting critical applications with it or a stack just like it.
The agentic era
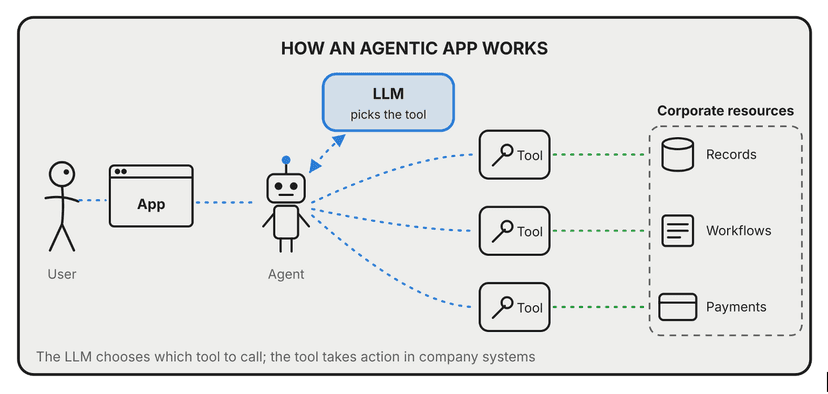
This era has brought about a shift in the development patterns. Teams are building agentic applications, where an agent's capability are packaged as tools it can call. A large language model (LLM) decides which tool to use, and in what order, to fulfill a user's request.
Just as teams in the 90s build web applications, teams today are using and building tools for agents. These tools connect agents to the organization's applications and data so they can take meaningful action inside the enterprise.
The intent is novel, but it brings about a sea of challenges around security. LLMs are probabilistic. How to credential an agent properly? How do we ensure only proper actions happen? Who determines what is proper and how do we move from probabilistic actions to deterministic-access-controlled actions?
Agentic access control
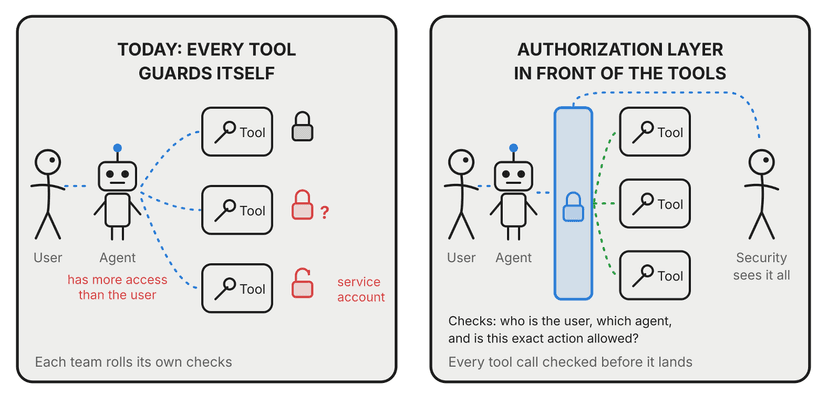
Options for credentialing agents to take action and to get them functional is not challenging. Properly securing this access, though, is. With various teams rushing to deploy agentic applications, it can get complicated to implement uniform security. I can use a service account to credential an agent, but a service account may have over-provisioned access. Maybe multiple service accounts with different levels of authorization are the answer? Maybe I use agentic guardrails - but guardrails are yet another layer of the probabilistic realm with the intent of improving control. Guardrails are not deterministic access control. Maybe the implementation needs to use users' authorization to limit scope, but this may not be possible for all use cases. Maybe a hybrid approach will work better? Oh, I know which standard to use for my agentic application, but which options within that standard are necessary for proper security?
So many options and decisions. Which team makes these decisions, and can they say that access is being deterministically enforced?
How can a CISO/CIO instill confidence in their board?
The stakes are much higher this time:
The caller is not deterministic. An LLM, not a fixed code path, decides which tool runs. Prompt injection, hallucinations, among others, can steer it towards actions nobody intended. or maybe it is a malicious action intent to begin with.
Identity is layered. Every call involves a user, an agent action for that user, and a tool action on a downstream system. Each hop has to carry the right identity and the right scope.
Service accounts are in use. There are use cases where the only option is to use a service account. How do you handle appropriate actions when the intended authorizations vary based on the user invoking an agent? For SaaS accounts, management of per user keys and authorizations can become very tricky very quickly.
Tools take action. This is not just a conversation with a user. Tool actions provide a direct path into enterprise systems and proper, manageable authorizations must be in place.
Policy is scattered. Various team trying to build and secure their agents for an application. Security teams have no easy way to determine security policies in play for an agent or application.
Central Visibility is lacking. Many teams are building agentic applications. Do security teams have visibility into all? How is security explained? When teams build their own authorization layers for the toolset, those same challenges, and more, come back in, as in the 90s with the explosion of web.
The answer then is the answer now
The lessons from web access management apply directly in the agentic era. Developers should focus on what their tools do, and let the dedicated agentic access layer handle securing the agentic eco system. If an agentic call reaches the tool, it has already been authenticated, authorized, and logged.
An agentic access layer should:
Authenticate every party. Verify a pre-authenticated users and require authentication for agents.
Continuously Authorize each tool call against central policies, at the level of specific action and data involved, not just "can this agent reach this tool service."
Propagate delegated identity, so appropriate authorizations are granted to an agent that can work in autonomous or delegated mode with appropriately scoped credentials.
Runtime visibility and control are essential in this agentic era where access and authorizations can change rapidly.
Record a full audit trail linking each action back to the user request and agent that triggered it.
Web access management gave enterprises the confidence to put hundreds of applications on the web. An access management layer for agents does the same for this agentic era - let teams build agents and tools quickly while security teams centrally secures access with deterministic policies. Organizations that learned this lesson in the 90s should not have to learn it again.
There are plenty of solutions emerging in this space. Broadcom's AgentMinder stands out with a robust agentic fabric. It is cloud-native and built to scale, running on Kubernetes across on-prem, private, and public clouds and integrating with existing authorization stacks though the AuthZEN standard. Central policy implementation with enforcement is a foundational security pattern, and a solution that scales while doing so is worth investing into.